Recognised by the cybersecurity innovation ecosystem.
QUPASS (QUantum PASSage) has participated in cybersecurity, deep-tech and innovation programmes and engagements that have helped test, validate and refine QuantumFold™ as it progresses toward enterprise and quantum-resilient security.
SHIELD 2026 — Grand Prize
WinnerCipherSprint under SHIELD 2026, organised by the Telangana Cyber Security Bureau, Telangana Police, with IIIT Hyderabad as academic partner.
Cybersecurity Grand Challenge 2.0
MVP WinnerWinner at the Idea and MVP stages in the Data Security category, followed by a Top-3 finish at the Final Product stage. The programme provided rigorous competition, mentorship and ecosystem exposure as QuantumFold™ evolved from concept toward an enterprise-ready platform.
Proprietary data-protection technology
QuantumFold™ incorporates proprietary QUPASS technologies including Vault-less Tokenization (VLT) and Structure-Preserving Scoped Tokenization (SPS-T).
- DPIIT Recognised Recognised by the Department for Promotion of Industry and Internal Trade (DPIIT), Government of India.
- CCoE Incubation Incubated by the Cybersecurity Centre of Excellence (CCoE), a joint initiative of the Government of Telangana and the Data Security Council of India (DSCI).
- Microsoft for Startups Part of the Microsoft for Startups ecosystem, supporting our technology and international growth journey.
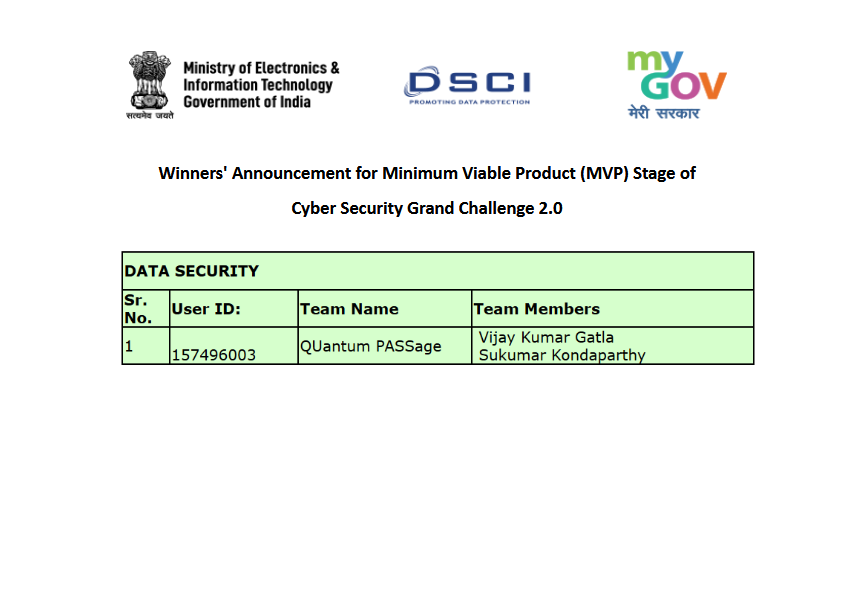
Named in the MeitY / DSCI Cyber Security Grand Challenge 2.0 winners' list in Data Security Category.
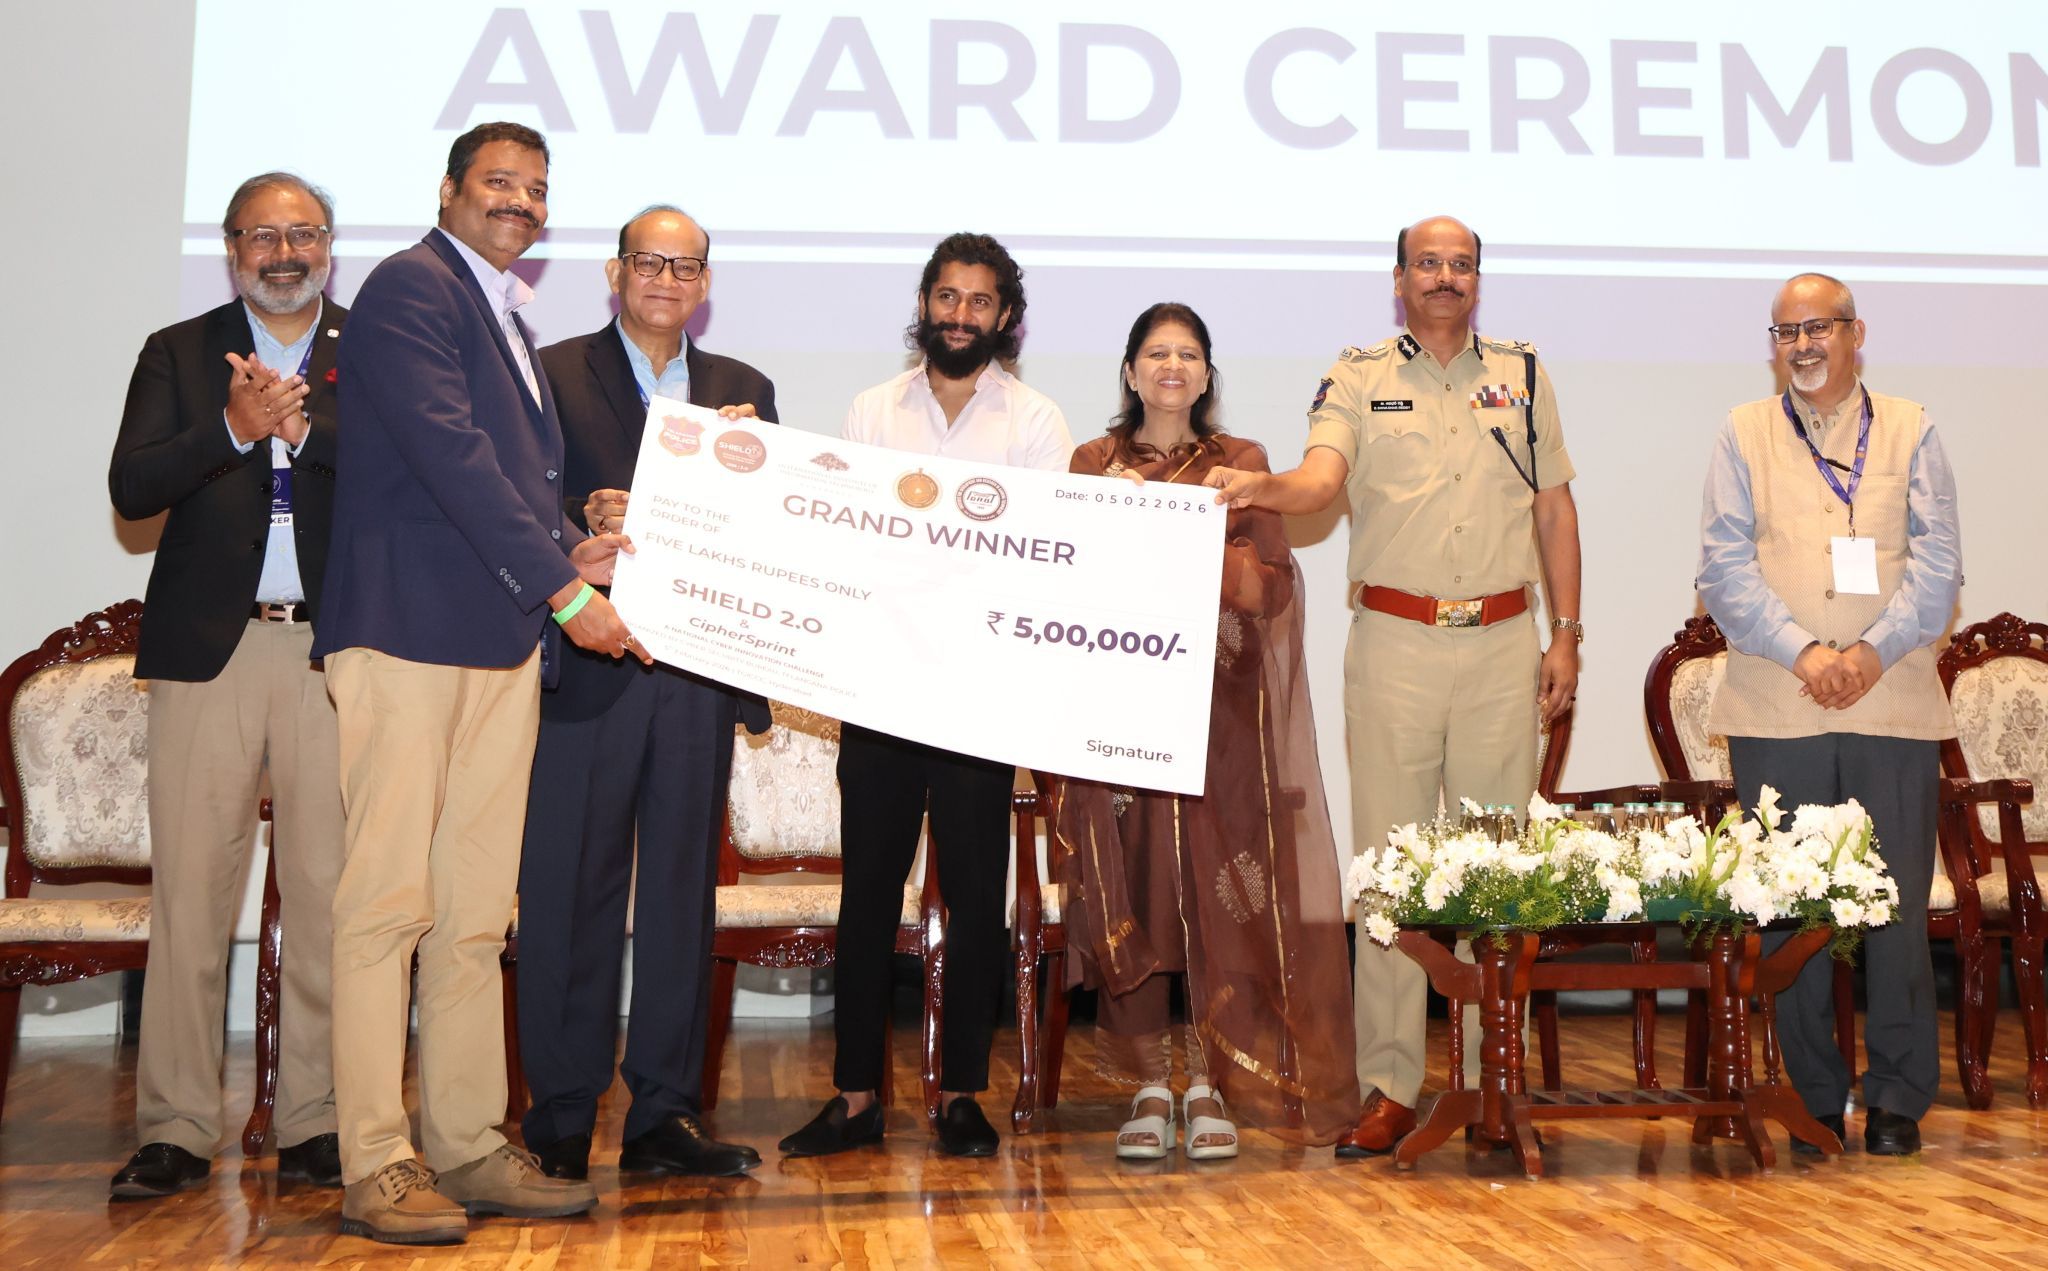
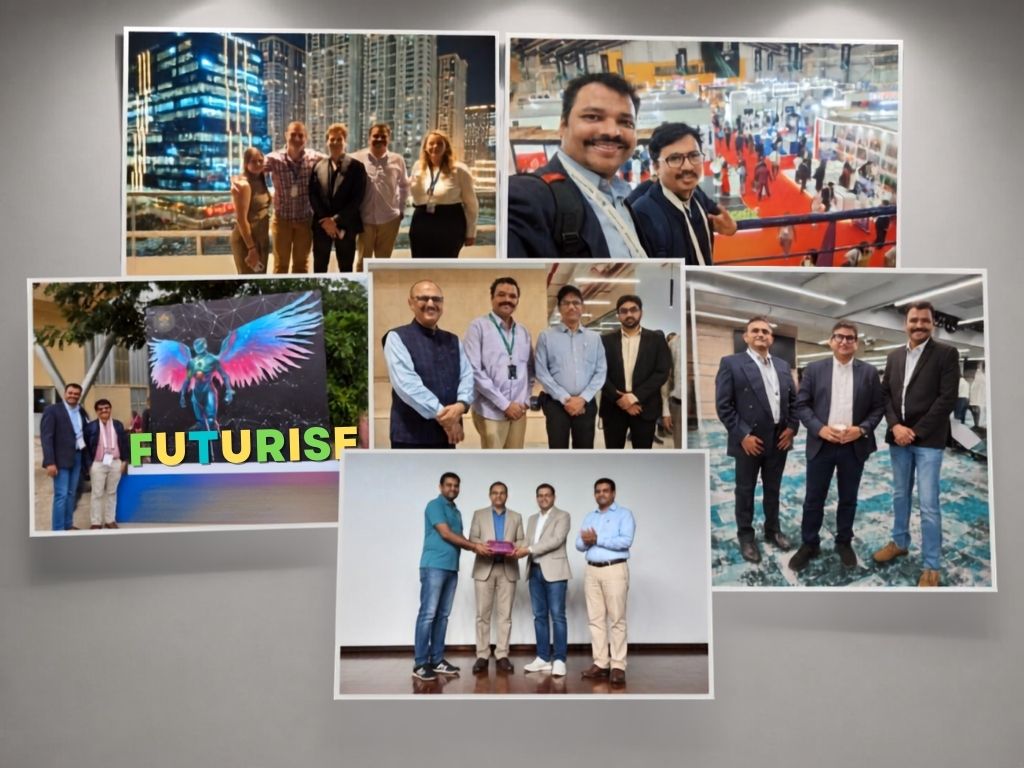
SHIELD 2026 — CipherSprint Grand Prize awarded on stage.
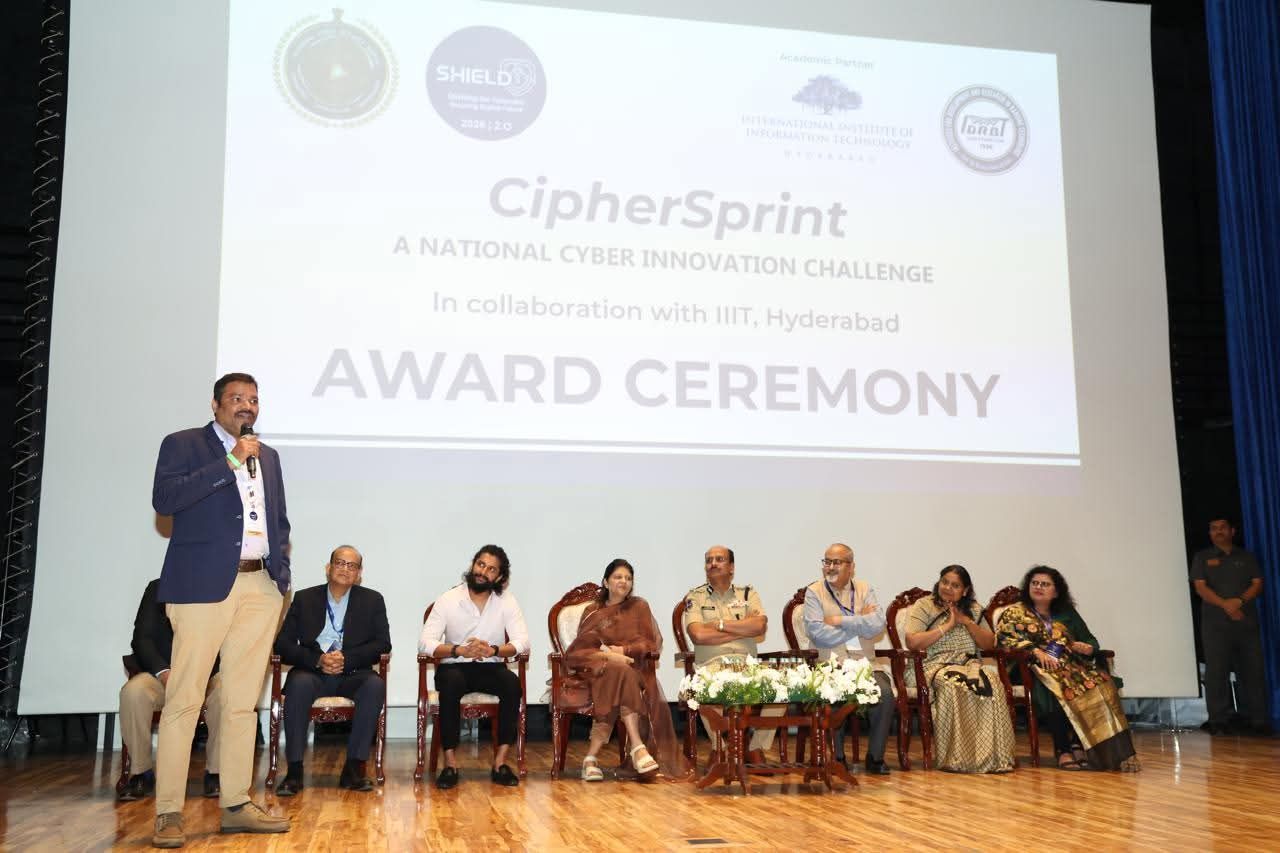
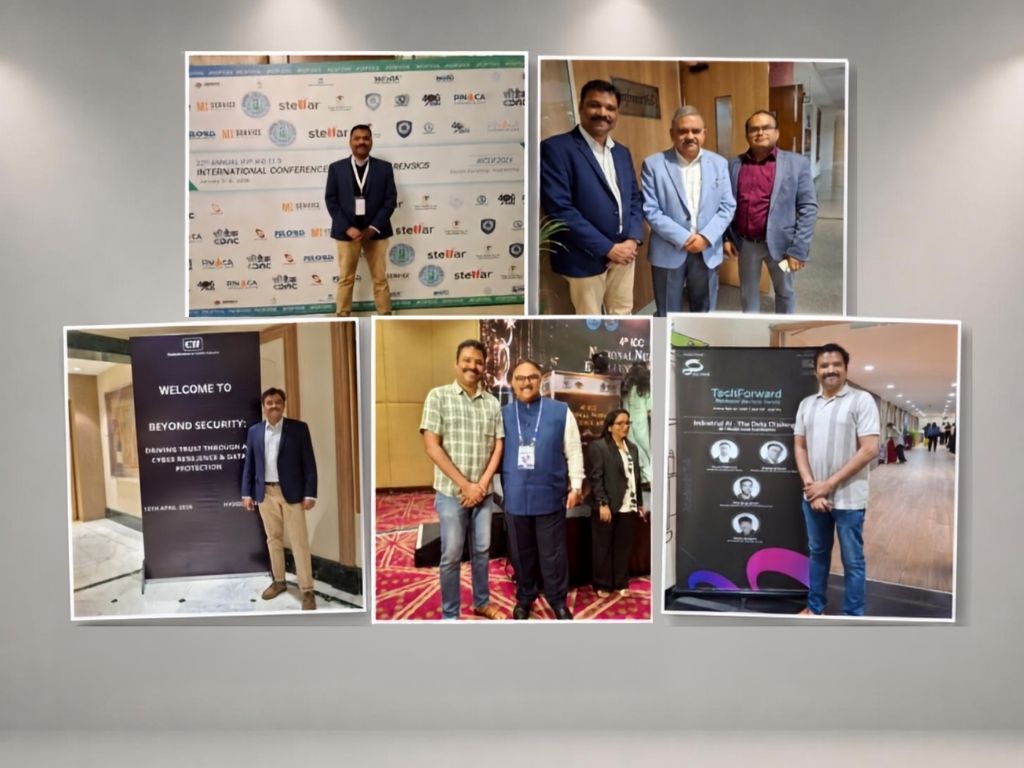
CipherSprint — a national cyber innovation challenge with Telangana Cyber Security Bureau, Telangana Police, IDRBT, and IIIT Hyderabad.
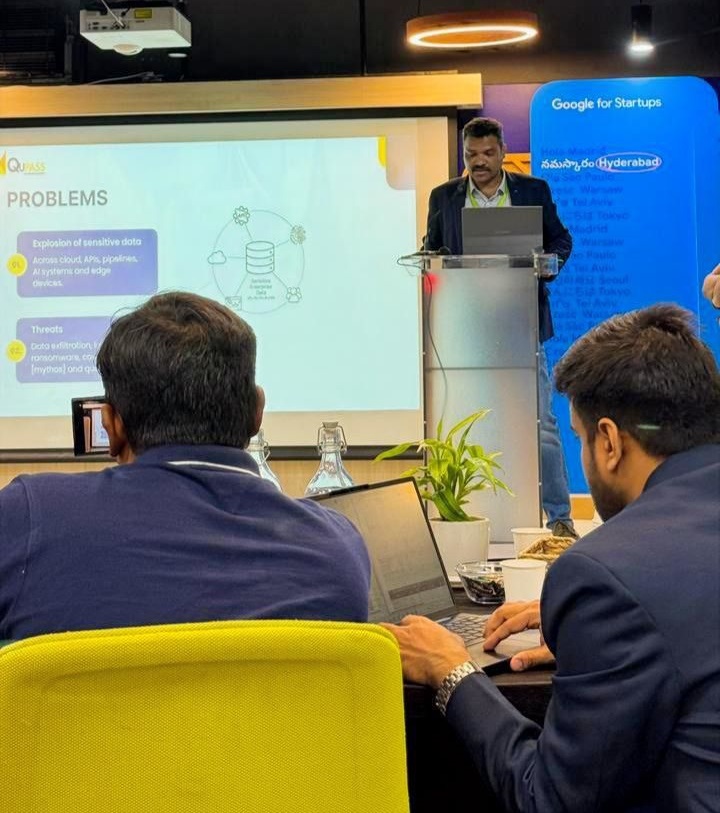
Presenting the problems, QuantumFold™ solves to the startup ecosystem.
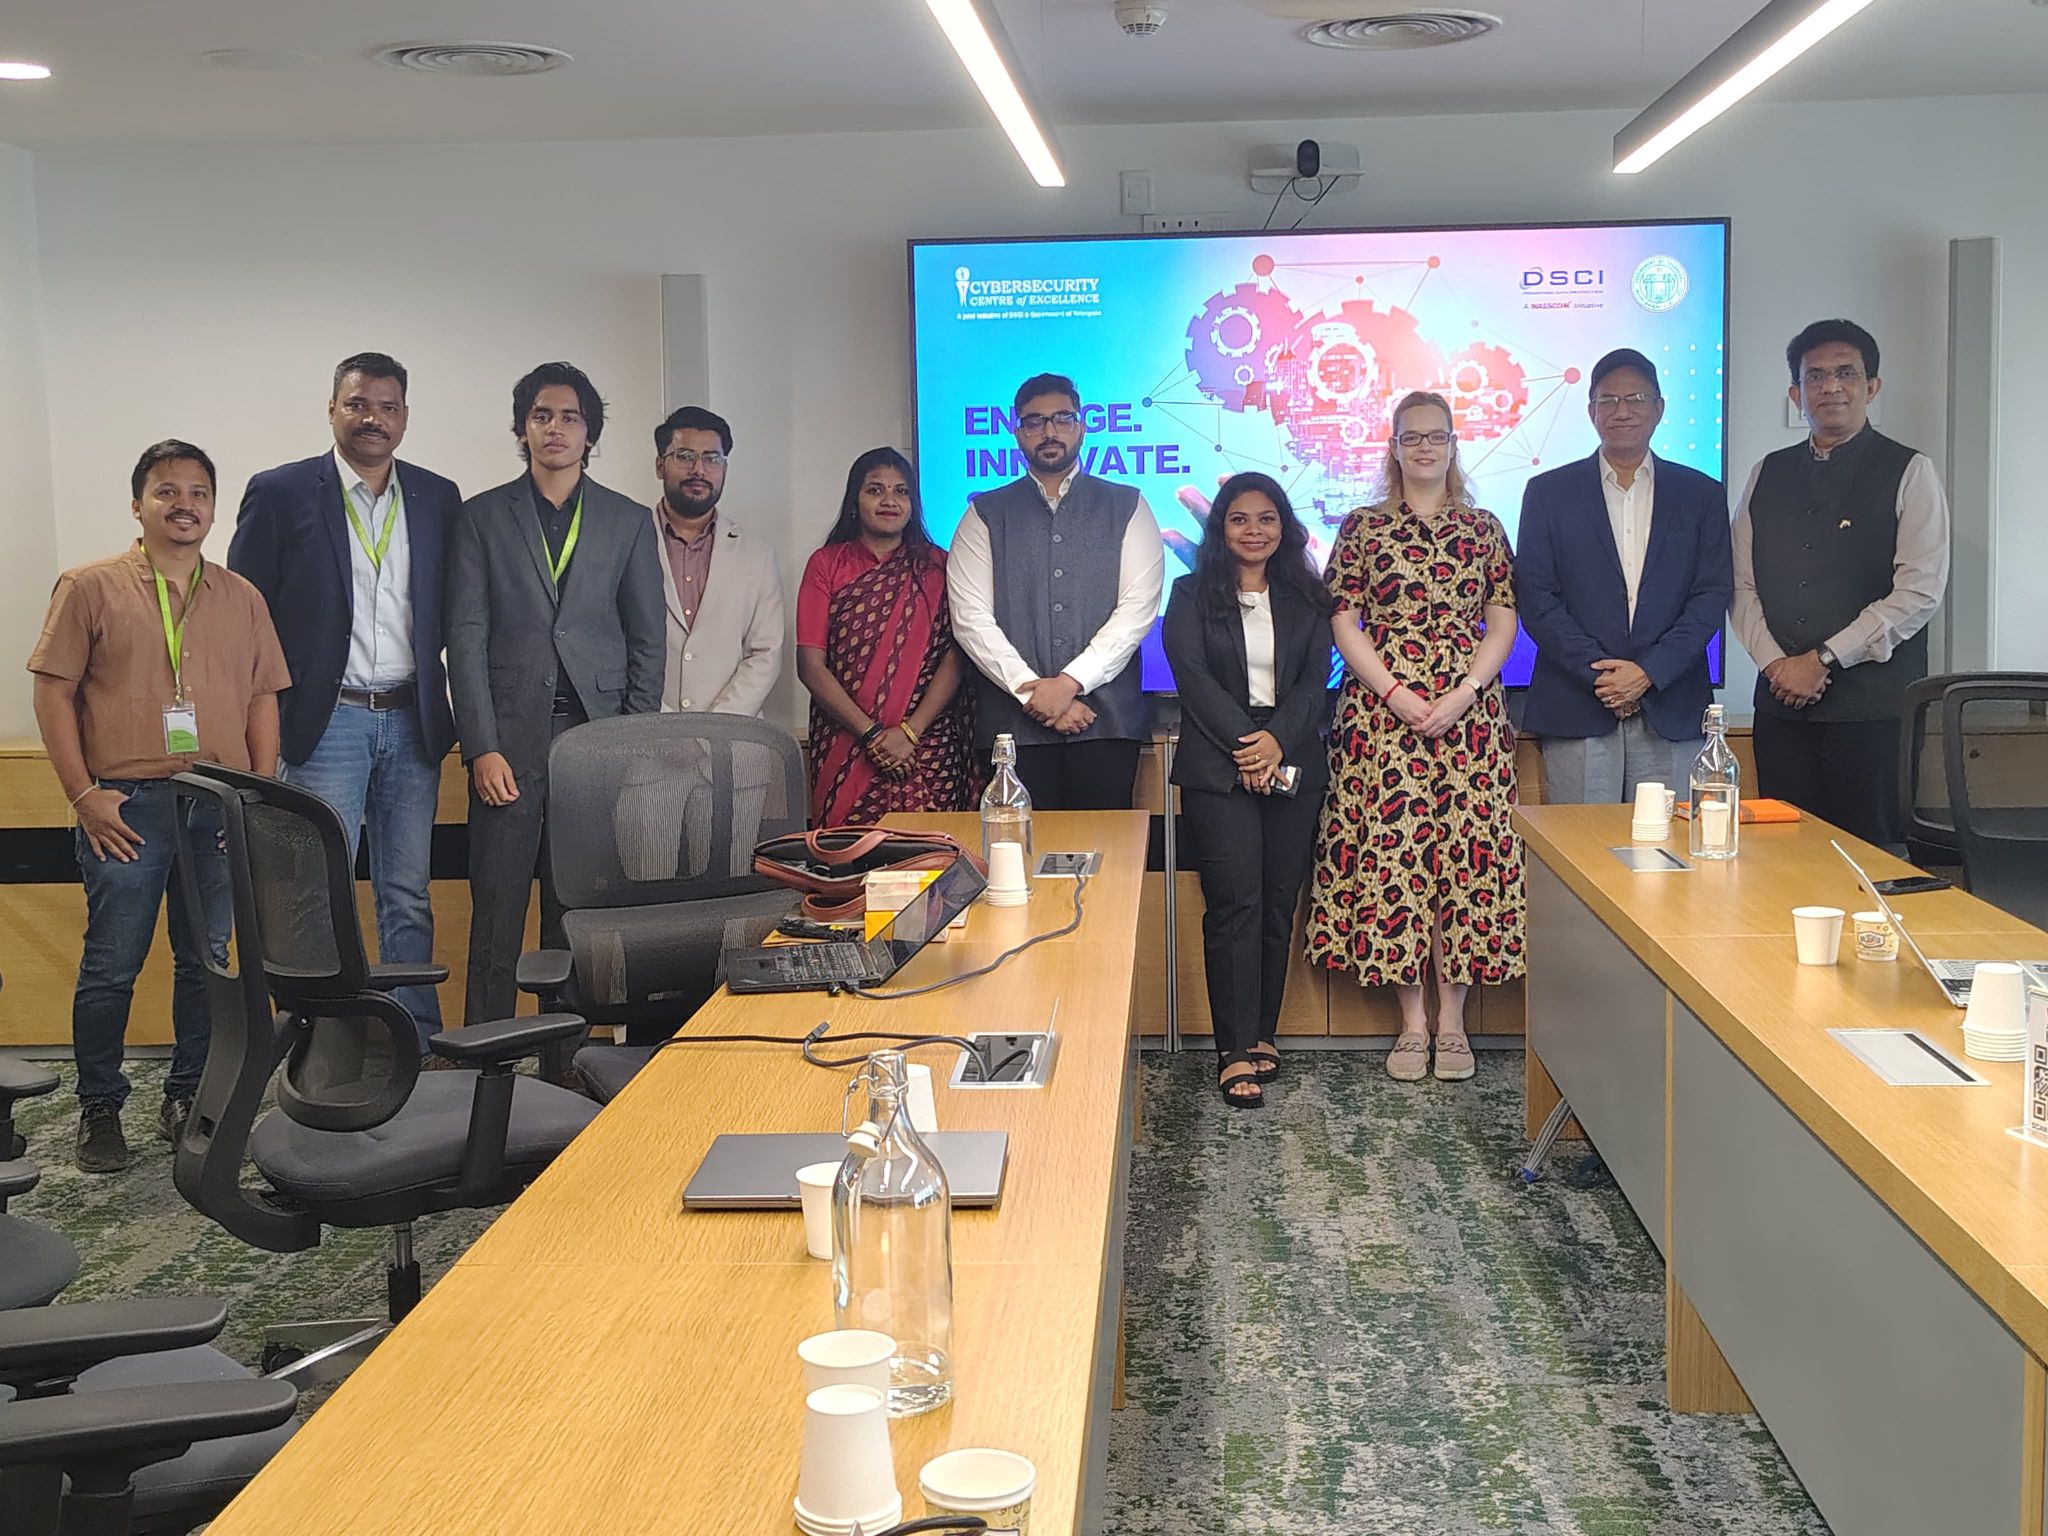
Engaging at the Cybersecurity Centre of Excellence (DSCI & Govt. of Telangana).
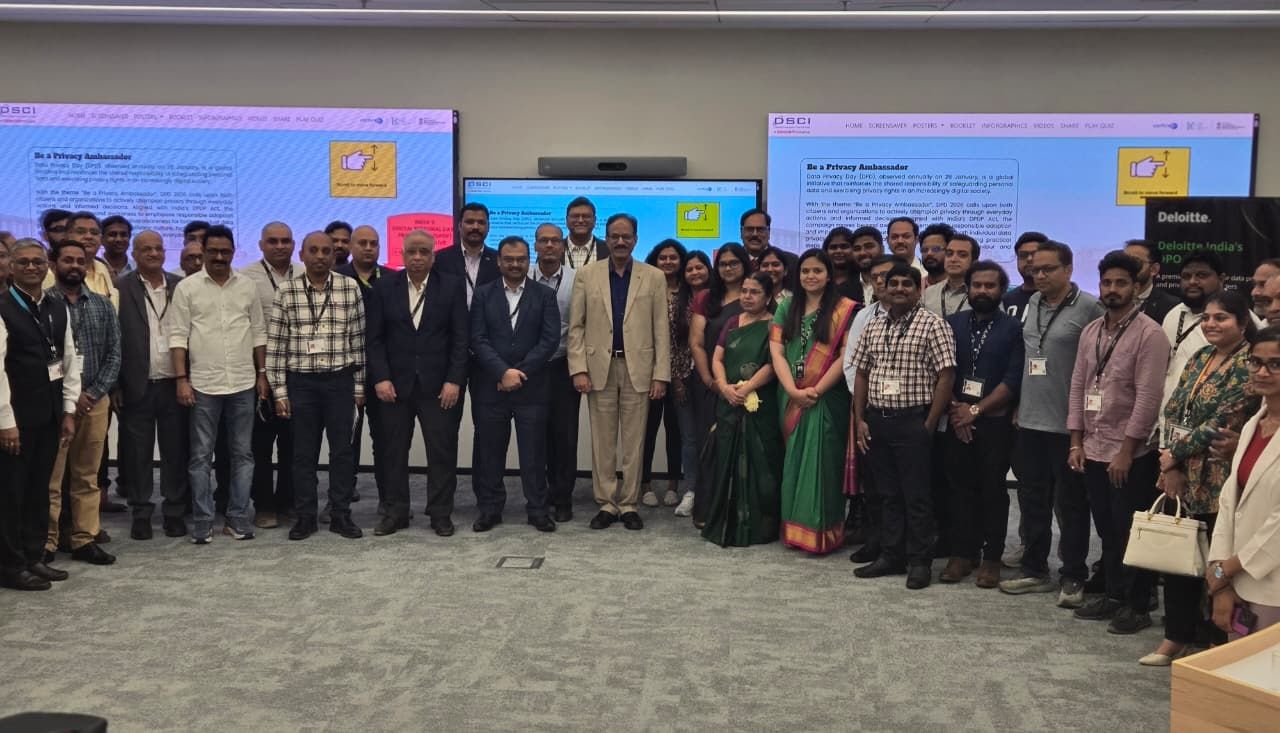
Part of the wider data-protection and privacy community.
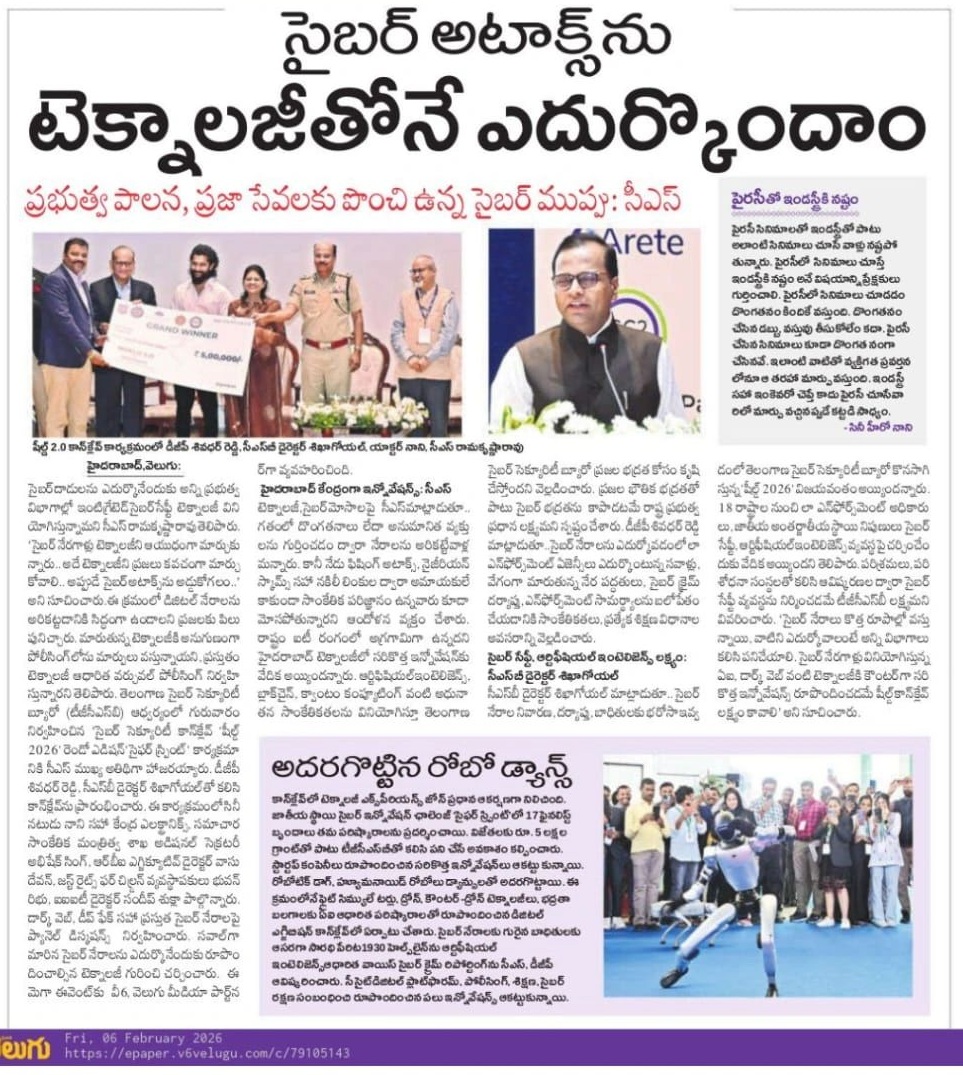
SHIELD 2.0 — Ciphersprint's Newspaper Coverage.
Protect sensitive data without giving up its value.
We work with enterprises, governments, technology companies, system integrators, cybersecurity ecosystems and AI/data organizations addressing increasingly demanding data-security and quantum-resilience requirements.
Questions about QuantumFold™
A concise view of how QuantumFold™ approaches data protection across applications, databases, analytics, AI and quantum-resilient security.
What is QuantumFold™?
QuantumFold™ is QUPASS's data-centric security platform for protecting sensitive information across applications, databases, analytics and AI. It brings application data protection, database protection, policy enforcement and protected analytics into a common protection architecture, with an approach that extends into AI and RAG workloads.
What is data-centric security?
Data-centric security places protection and access policy closer to the data itself rather than relying only on controls around the surrounding application or network. The objective is to protect sensitive information while preserving the structure, context and utility that legitimate applications, users and analytics workflows require.
How does QuantumFold™ protect application data?
QuantumFold™ provides developer-ready protection APIs for operations such as encryption, tokenization, masking and redaction. Applications can authenticate, obtain the required credentials or tokens, and invoke protection services from the programming environment they already use.
Does QuantumFold™ protect PostgreSQL and MySQL databases?
Yes. QuantumFold™ Transparent Database Protection is designed to work with PostgreSQL and MySQL through a database-protocol-aware proxy. The proxy governs the access path and policy, while the protection engine performs the underlying data-protection operations.
Can protected data still be used for analytics?
QuantumFold™ is designed with data utility in mind. Protected data can continue to support operational queries, dashboards, reports and analytics workflows where the required protection and access policies permit it. The aim is to reduce the trade-off between protecting sensitive information and keeping it useful.
What is QuantumFold™'s approach to AI and RAG data protection?
QuantumFold™ extends data-centric protection into AI workflows. Its current direction covers protection before sensitive information reaches an AI model or API, policy applied to data retrieved into AI context, controlled access for AI agents, and inspection of AI-generated output before release.
Can QuantumFold™ run inside an enterprise environment?
Yes. QuantumFold™ supports a customer-resident Enterprise Data Plane for regulated and enterprise environments. The protection runtime can be deployed within the customer's infrastructure, allowing the sensitive-data processing path to remain inside the customer's security boundary.
Does QuantumFold™ support on-premises and private-cloud deployment?
QuantumFold™ supports multiple deployment models, including cloud / SaaS, customer-resident enterprise deployment, hybrid environments, and private or sovereign environments. The appropriate model depends on the customer's operational, security and data-governance requirements.
What is vault-less tokenization?
Vault-less Tokenization is a QUPASS technology designed to avoid the dependency on a traditional centralized token vault. It is intended to support scalable data-protection architectures while retaining practical control over protected data.
What is Structure-Preserving Scoped Tokenization (SPS-T)?
Structure-Preserving Scoped Tokenization, or SPS-T, is a QUPASS technology designed for controlled protection while preserving characteristics of protected data that may be important to applications and downstream processing. It forms part of QuantumFold™'s approach to maintaining data utility under protection.
Is QuantumFold™ being developed for the post-quantum era?
Quantum resilience is part of QuantumFold™'s forward-looking security direction. QUPASS is developing the platform with a path toward post-quantum cryptography and longer-term resilience against emerging quantum threats, while continuing to address the data-protection needs of today's enterprise environments.